Guillemet helped establish Ledger’s Donjon security lab and says his departure has been planned for months.
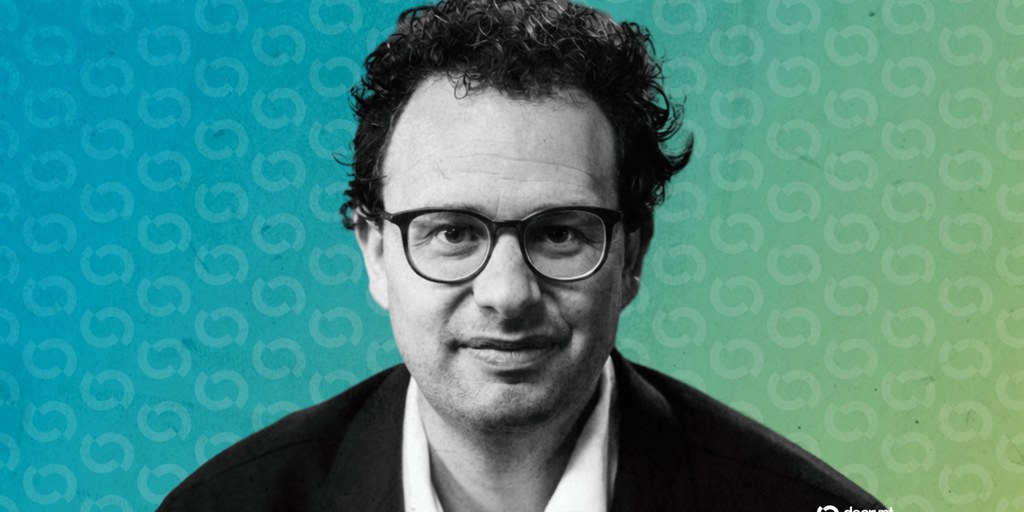
Ledger chief technology officer Charles Guillemet announced he will be leaving the company at the end of 2026, after nine years at the company.
In a post on LinkedIn on Thursday, Guillemet said he joined as chief security officer in December 2017, around three years after Ledger was founded. He launched Ledger Donjon, the company’s attack lab, a year later.
“We’ve been preparing this transition for many months, so Ledger’s teams, partners and roadmaps are ready. I’m bullish on Ledger’s future,” said Guillemet.
Guillemet has been a central figure in Ledger’s security operations, first as chief security officer and later as chief technology officer. He helped establish the Ledger Donjon attack lab, which tests hardware and software vulnerabilities. According to Guillemet, Ledger devices now secure roughly 20% of the world’s crypto assets.
“The threat landscape changed too. AI is making attacks cheaper, faster and easier to scale,” he added.
“The question we spent a decade answering for crypto (how do you protect what matters when any device can be compromised?) is now a question for every company, every AI agent and every government.”
Guillemet did not disclose details of his next venture but said he was “building something new” and would “dedicate my time to solving this security mess.”
Guillemet’s announcement comes weeks after Ledger disclosed that attackers had modified genuine hardware wallets with hidden components designed to capture users’ recovery phrases, and slipped the devices into authorized resellers.
The tampering cases were initially reported in Asia, with subsequent incidents identified in Europe and the United Arab Emirates.
Related: Ledger hardware implant saga reaches Dubai’s Virgin Megastore